GDPR Compliant Cloud in Luxembourg: A Strategic Guide
Build a GDPR compliant cloud in Luxembourg with Microsoft Fabric. Our guide helps you meet CNPD rules, ensure data residency, and turn compliance into an adv...
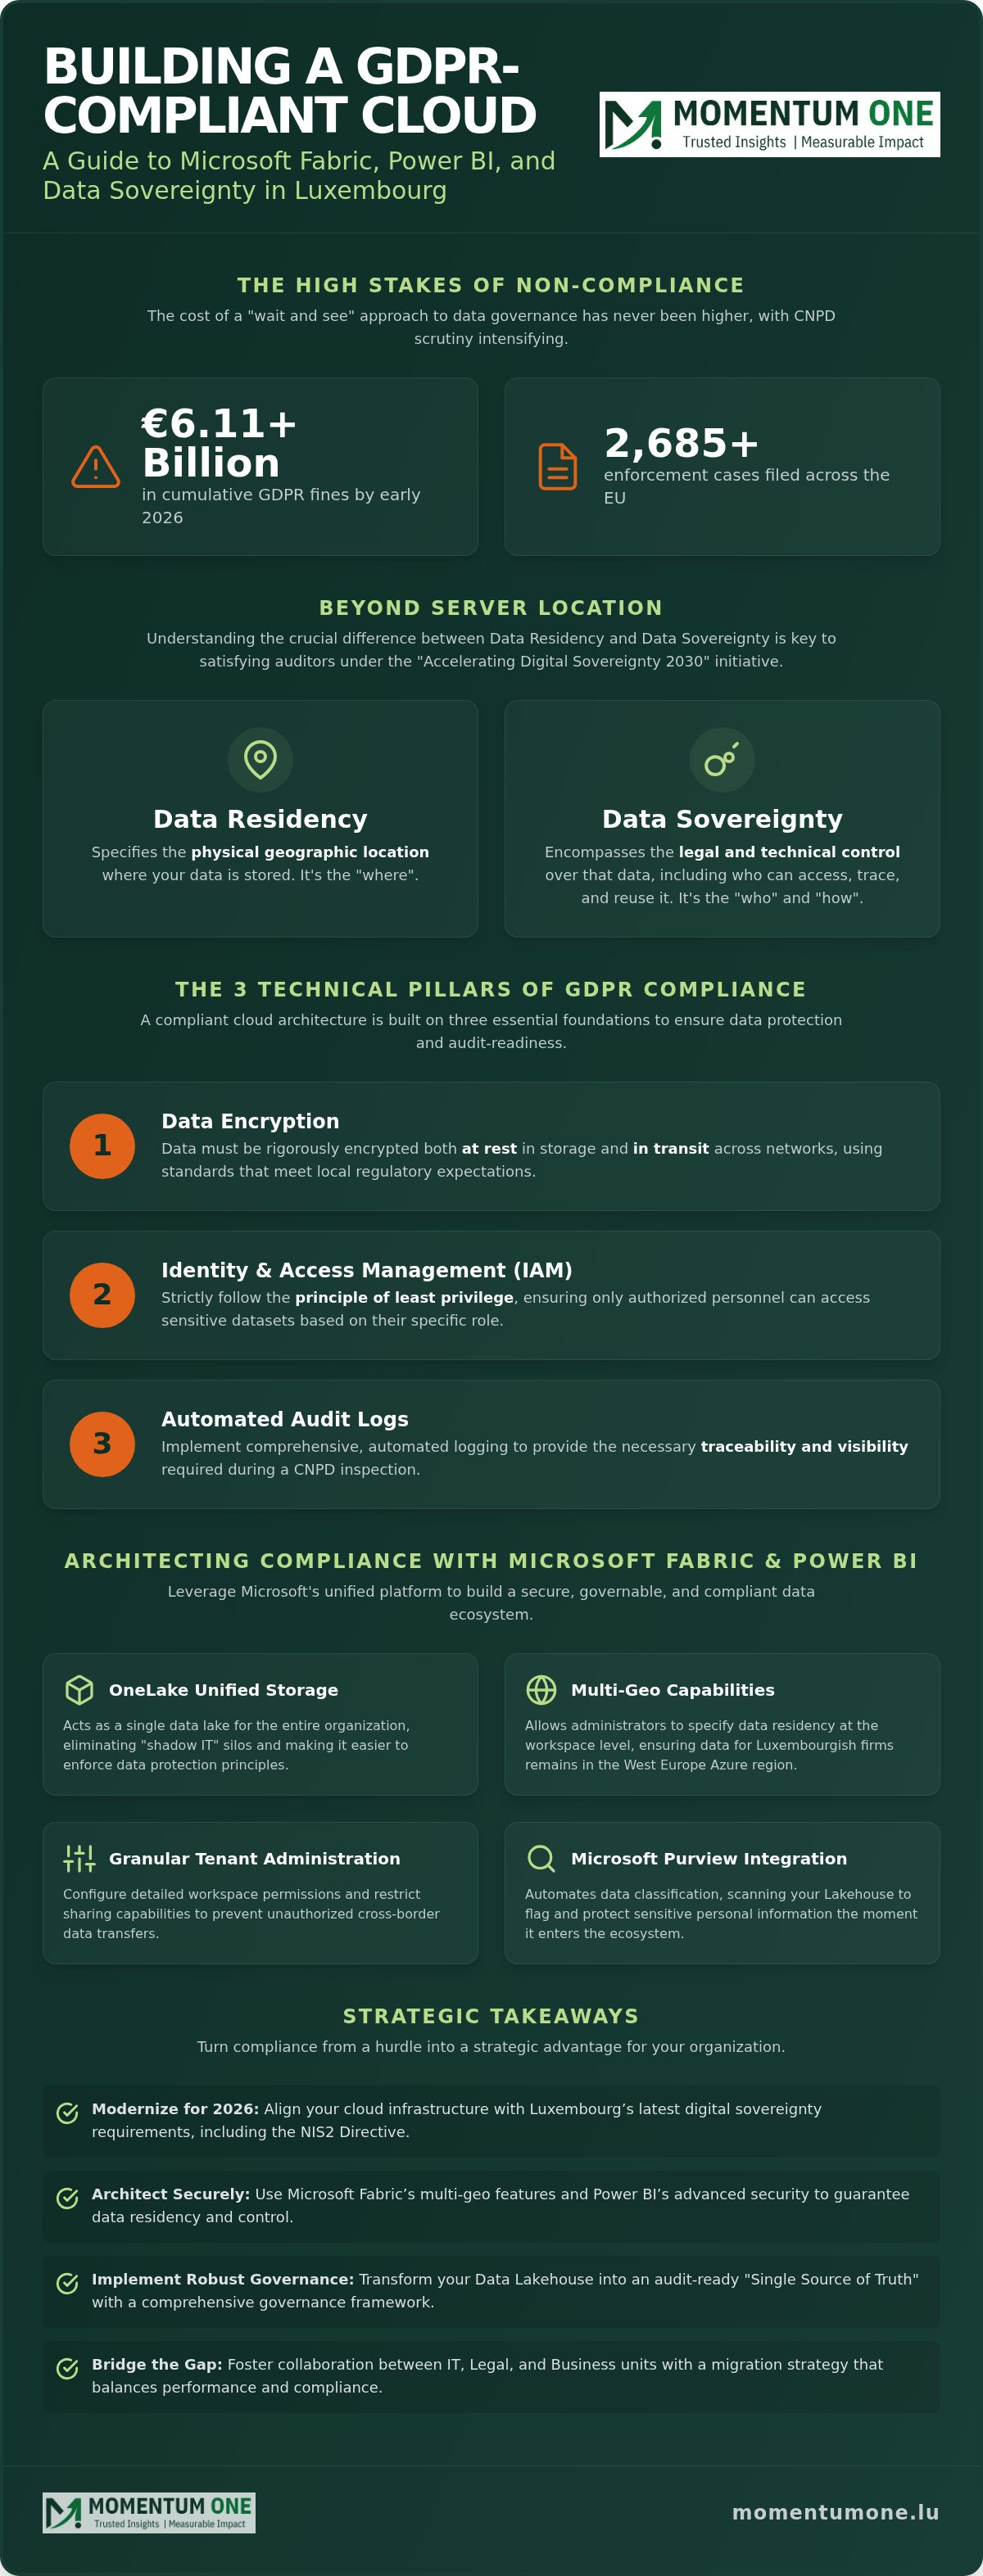
- Modernize your approach to CNPD standards by aligning your cloud infrastructure with Luxembourg’s latest 2026 digital sovereignty requirements.
- Architect a secure data ecosystem using Microsoft Fabric’s multi-geo features and advanced Power BI security protocols to ensure data residency.
- Master the technical nuances of a gdpr compliant cloud luxembourg , going beyond server location to secure administrative access and encryption keys.
- Implement a robust 5-step governance framework that transforms your data lakehouse into an audit-ready "Single Source of Truth."
- Bridge the gap between IT, Legal, and Business units through a collaborative migration strategy that prioritizes both performance and compliance.
With cumulative GDPR fines surpassing €6.11 billion across more than 2,685 cases by early 2026, the cost of a "wait and see" approach to data governance has never been higher. You've likely felt the tension between the need for high-performance analytics and the strict oversight of the CNPD. It's a common struggle; many organizations in the Grand Duchy worry that adopting a US-based provider like Microsoft means compromising on sovereignty or risking a devastating audit. We understand that complexity often leads to paralysis, but staying on-premise isn't a viable long-term strategy for growth.
This guide provides the clarity you need to build a robust, gdpr compliant cloud luxembourg ecosystem using Microsoft Fabric and Power BI. We'll move past the uncertainty of the Schrems II legacy and show you how to configure a Data Lakehouse that meets the latest standards, including the "Accelerating Digital Sovereignty 2030" initiative. You'll learn how to implement a governance framework that satisfies auditors without sacrificing the speed or accuracy of your business intelligence. We're diving into the technical and regulatory requirements you need to master to turn compliance from a hurdle into a strategic advantage.
Navigating GDPR Compliance for Cloud Environments in Luxembourg
Luxembourg's path to the cloud has matured significantly. In 2026, a gdpr compliant cloud luxembourg is defined by more than just where your servers sit. It's about a comprehensive governance framework that aligns with the General Data Protection Regulation (GDPR) while leveraging the scalability of modern platforms. The National Commission for Data Protection (CNPD) has shifted its focus. They've moved from merely questioning cloud adoption to scrutinizing the specific technical controls used to protect personal data within those environments. This evolution allows organizations to move past on-premise anxiety by adopting cloud-native strategies that often offer better security than traditional data centers.
Data residency is often confused with data sovereignty. While residency specifies the physical location of data, sovereignty encompasses the legal and technical control over that information. Under the government's "Accelerating Digital Sovereignty 2030" initiative, true sovereignty requires managing data access, traceability, and reuse. Simply hosting data within the borders of the Grand Duchy isn't enough to satisfy auditors if administrative access remains opaque or if encryption keys are managed by a third party without oversight.
Understanding the 2026 Regulatory Landscape
The regulatory environment in 2026 is defined by the full implementation of the NIS2 Directive, which became effective in Luxembourg on May 10, 2026. This law introduces stricter cybersecurity obligations for a wider range of entities. Standard cloud offerings provide the basic infrastructure, but sovereign cloud configurations add essential layers of control. This distinction is critical for local firms navigating the aftermath of high-profile cases, like the March 2026 annulment of the Amazon GDPR fine on procedural grounds. That case has kept the CNPD's enforcement strategies and the need for rigorous documentation in the spotlight.
The Technical Pillars of GDPR Compliance
Achieving compliance requires three technical pillars. First, data must be encrypted at rest and in transit using standards that meet local regulatory expectations. Second, Identity and Access Management (IAM) must follow the principle of least privilege, ensuring only authorized personnel can access sensitive datasets. Finally, automated audit logs are no longer optional. They provide the visibility needed during a CNPD inspection. For those looking to build these foundations, a robust Data Warehouse & Lakehouse Design is the essential starting point for an audit-ready ecosystem that doesn't trade performance for security.
Microsoft Fabric and Power BI: Architecting Compliance in the Cloud
Microsoft Fabric simplifies the path to a gdpr compliant cloud luxembourg by unifying data storage, engineering, and analytics under one governance umbrella. Central to this is OneLake, which acts as a single, logical data lake for the entire organization. By consolidating data assets, you eliminate the "shadow IT" silos that often lead to compliance breaches. This centralized approach makes it significantly easier to enforce the data protection principles outlined in the Official text of the GDPR, such as data minimization and purpose limitation. It's about creating a transparent environment where every byte of data is accounted for and governed systematically.
Data Residency and Tenant Administration
Power BI and Fabric allow administrators to specify exactly where data resides at the workspace level. For Luxembourgish firms, this means utilizing Multi-geo capabilities to ensure data stays within the West Europe Azure region, which serves our local market. Tenant administration is your first line of defense. By configuring granular workspace permissions and restricting sharing capabilities, you effectively prevent unauthorized cross-border transfers. Integrating Microsoft Purview further strengthens this by automating data classification. Purview scans your Lakehouse to ensure sensitive personal information is flagged and protected the moment it enters the ecosystem. If you're looking to transition your legacy systems, our Fabric Migration & Modernization experts can guide you through these critical configuration steps.
Optimizing Performance Without Compromising Privacy
High-performance analytics shouldn't suffer because of security constraints. Row-Level Security (RLS) remains the gold standard for ensuring users only see the data they're authorized to access within Power BI. However, complex RLS logic can sometimes impact report responsiveness if not handled correctly. This is where specialized Power BI Consulting & Governance becomes a strategic asset. Optimizing DAX measures within secured datasets ensures that your dashboards remain fast and reliable without leaking sensitive information. By designing audit-ready data models from the start, you maintain a "Single Source of Truth" that satisfies both your business analysts and your legal department. This methodical balance is the hallmark of a mature, compliant cloud strategy in the 2026 landscape.
The Data Sovereignty Challenge: Beyond Server Location
Pinning data to a specific geography is just the baseline for modern compliance. To build a truly gdpr compliant cloud luxembourg, you have to address technical and operational sovereignty. Technical sovereignty means ensuring that your data remains unreadable to the cloud provider, even if administrative access is required for maintenance. This is achieved through Customer Managed Keys (CMK) and Customer Lockbox, where you hold the power to grant or deny access to Microsoft engineers during support scenarios. It's about moving from a model of "trust" to a model of "verify" through technical enforcement.
Operational sovereignty is equally vital. It's the ability to maintain business continuity and migrate workloads without being locked into a single vendor's ecosystem. The EU Cloud Services Scheme (EUCS) is increasingly influencing how local enterprises select their stacks, pushing for higher transparency in how providers handle metadata and administrative logs. When moving beyond simple residency, referring to a comprehensive GDPR compliance checklist helps align these technical controls with your broader legal obligations. This ensures that your cloud strategy isn't just a technical upgrade, but a legally defensible framework.
Managing Third-Party Risk in the Cloud
Evaluating a Cloud Service Provider (CSP) requires looking past their marketing brochures. You need to verify how they mitigate extraterritorial data access, particularly in light of the US Cloud Act. As a Microsoft Solutions Partner, we help you audit these technical measures. We ensure your Data Architecture Modernization includes robust encryption and identity silos that keep your data within your control. This proactive approach reduces the risk of "scope creep" where data might accidentally become accessible to unauthorized third parties during routine operations.
Sovereign Data Sharing and Data Spaces
Luxembourg is leading the way with the Data Spaces Hub, which promotes secure, cross-sector data sharing. Microsoft Fabric is uniquely positioned to support this through its "shortcuts" and secure pipelines. Instead of copying data and creating new compliance risks, you can share access to a single source of truth without moving the underlying files. Transitioning from a legacy on-premise warehouse to a modern Data Warehouse & Lakehouse Design allows you to participate in these emerging data ecosystems. You gain the ability to collaborate with partners while maintaining the strict governance and performance your auditors expect in a 2026 regulatory environment.
A Robust Data Governance Framework for Luxembourgish Enterprises
Building a gdpr compliant cloud luxembourg requires more than just high-end encryption; it demands a living governance framework. Technology provides the walls, but governance provides the rules for who enters and what they can do. For corporate teams in the Grand Duchy, this means moving beyond ad-hoc data management to a structured lifecycle approach. An audit-ready environment is the result of deliberate planning that bridges the gap between technical capability and legal necessity. To ensure your cloud ecosystem remains compliant under the scrutiny of a CNPD audit, we recommend following this 5-step checklist:
- Inventory & Classification: Use automated tools to discover and tag personal data across your OneLake environment.
- Access Control: Implement Row-Level Security to restrict data visibility based on specific user roles and geographic locations.
- Retention Policies: Automate the deletion of datasets that no longer serve their original purpose to avoid storage liabilities.
- Audit Logging: Maintain immutable records of data access and administrative changes for at least one year.
- Periodic Reviews: Conduct quarterly assessments to ensure your configurations still meet evolving national standards.
Establishing Internal Governance Standards
Effective oversight starts with a Data Governance Council. This group shouldn't just be an IT committee; it must include representatives from legal, compliance, and business units. By Establishing an Effective Power BI Governance Framework, you create a clear line of accountability. Data owners are typically business leaders who understand the risk of the information, while data stewards are the technical experts who implement the security protocols. This partnership ensures that technical settings in Microsoft Fabric align with real-world business needs and regulatory requirements.
Continuous Compliance and Monitoring
The human element is often the weakest link in any security strategy, which is why automated monitoring and data literacy are essential. Microsoft Fabric offers integrated tools to set up automated alerts for data sensitivity violations, flagging unauthorized sharing or unusual access patterns in real-time. Regular architectural reviews also help identify inefficient DAX queries that might be slowing down reports or accidentally bypassing security filters. If your internal team is stretched thin, our Managed Services provide the ongoing security oversight and technical support needed to maintain a high-performance gdpr compliant cloud luxembourg.
Implementing Your Compliant Cloud Strategy with Momentum One
Transitioning to a gdpr compliant cloud luxembourg involves more than just selecting the right tools; it requires a partner who understands the intersection of technology and local regulation. At Momentum One, we act as a steady hand for organizations navigating this shift. We specialize in bridging the gap between IT, legal, and business units to ensure that technical configurations satisfy regulatory requirements without hindering operational performance. Our role is to simplify the complexity of the Microsoft ecosystem, turning abstract compliance goals into a functional, high-performance data environment.
Strategic Migration and Design
Our approach begins with a focus on robust architecture. We design custom Data Warehouse & Lakehouse Design solutions that prioritize security from the first line of code. By leveraging our Fabric Migration & Modernization Services, your organization can move legacy workloads into a unified environment that scales effortlessly. We ensure that as your data volume grows, your compliance risk doesn't grow with it. This involves configuring OneLake and multi-geo settings to align with the residency requirements we discussed earlier, ensuring your "Single Source of Truth" remains audit-ready and legally defensible.
Expert Support and Partnership
As a certified Microsoft Solutions Partner, we provide deep technical expertise that covers the entire data lifecycle. Whether you need DAX Optimization to speed up secured reports or a full-scale cloud transformation, our team is dedicated to your long-term success. We don't believe in "set and forget" solutions. Instead, we offer Training Solutions and managed services to ensure your staff remains literate in the latest governance protocols. This human-centric approach builds a culture of compliance that protects your organization from the inside out.
Maintaining a gdpr compliant cloud luxembourg is an ongoing journey that requires constant vigilance and technical precision. We help you stay ahead of CNPD expectations through regular architectural reviews and proactive monitoring. Our goal is to empower your business to use data as a strategic asset, free from the fear of regulatory fines or data breaches. If you're ready to modernize your infrastructure with a partner who values reliability and collaborative progress, Contact Momentum One for a Compliance-First Cloud Review today.
Building a Future-Proof Data Ecosystem in Luxembourg
Mastering the technical and regulatory nuances of a gdpr compliant cloud luxembourg strategy is no longer a luxury for local enterprises. It's a fundamental requirement for sustainable growth. By moving beyond simple data residency and embracing a sovereign governance framework, you transform compliance from a legal burden into a competitive advantage. You've seen how Microsoft Fabric and Power BI provide the tools to centralize your data while maintaining the granular control required by the CNPD. The path forward involves aligning your IT infrastructure with your legal obligations through a methodical, audit-ready approach.
As a certified Microsoft Solutions Partner with deep expertise in Microsoft Fabric and Lakehouse architecture, Momentum One acts as your steady hand. We bring a proven track record in Luxembourgish corporate data governance to every project, ensuring your transition is seamless and secure. Don't let regulatory complexity stall your innovation. Take the next step toward a high-performance, compliant future today.
Secure your data strategy with Momentum One's Power BI Consulting & Governance
Frequently Asked Questions
Is Microsoft Fabric GDPR compliant for use in Luxembourg?
Microsoft Fabric provides the technical infrastructure necessary to build a gdpr compliant cloud luxembourg environment, but compliance isn't automatic. It's a shared responsibility model. While Microsoft secures the underlying physical infrastructure, your organization is responsible for configuring identity management, encryption, and data lifecycle policies. Using features like Customer Lockbox and Microsoft Purview allows you to demonstrate the high level of control required by local regulators during a CNPD audit.
Does Luxembourg law require data to be stored on local servers?
Luxembourgish law doesn't mandate that all corporate data must stay on physical servers within the country, but it does emphasize data residency and sovereignty. Under the "Accelerating Digital Sovereignty 2030" initiative, the focus is on your ability to control and access your data. For most firms, hosting data in the West Europe Azure region is a standard practice that satisfies residency concerns while providing the performance benefits of a modern cloud stack.
What is the role of the CNPD in cloud data migrations?
The CNPD acts as the primary supervisory authority, ensuring that any cloud migration respects the fundamental rights of data subjects. They have the power to conduct unannounced on-site inspections and issue significant fines for non-compliance. Their role has evolved to scrutinize the technical governance of cloud environments. This means they look for clear documentation, robust audit logs, and evidence that you've performed a thorough Data Protection Impact Assessment before migrating.
How does Microsoft Fabric handle data residency requirements?
Microsoft Fabric handles residency through its Multi-geo capabilities, allowing you to specify the geographic location of your OneLake data at the workspace level. This ensures that sensitive information remains within the European Economic Area, specifically the West Europe region favored by Luxembourgish enterprises. By logically centralizing data while physically pinning its location, you maintain a gdpr compliant cloud luxembourg ecosystem that meets both technical performance needs and strict legal residency requirements.
Can Power BI reports be secured to meet strict GDPR privacy standards?
You can absolutely secure Power BI reports to meet the most stringent privacy standards by implementing Row-Level Security (RLS). RLS ensures that users only see the specific data rows they're authorized to view based on their role or department. When combined with granular workspace permissions and sensitivity labels from Microsoft Purview, Power BI becomes a powerful tool for maintaining privacy. It allows for high-level analytics without risking the exposure of sensitive personal information.
What are the common compliance pitfalls in cloud data warehouse design?
One of the most frequent pitfalls is failing to establish a clear "Single Source of Truth," which leads to fragmented data silos and "shadow IT." Without centralized governance, it's nearly impossible to track where personal data is stored or who has access to it. Other common issues include missing audit logs, poorly defined data retention policies, and over-privileged administrative accounts. These gaps create significant vulnerabilities that can lead to failed audits and regulatory penalties.
How do I ensure my DAX calculations don't bypass security filters?
To ensure DAX calculations don't bypass security, you must design your measures to be "RLS-aware." Some DAX functions, like those that ignore filters or calculate totals across the entire dataset, can inadvertently reveal information that should be hidden. We recommend testing all calculations against different user roles during the development phase. This methodical approach ensures that your performance-optimized reports never compromise the underlying security filters established in your data model.
Why is a Microsoft Solutions Partner necessary for GDPR compliance?
A Microsoft Solutions Partner provides the steady hand needed to navigate the technical complexity of cloud governance. While Microsoft provides the tools, a partner like Momentum One helps you implement them according to Luxembourg's specific regulatory landscape. We bridge the gap between IT, legal, and business units. This collaborative approach ensures that your Fabric migration and Power BI architecture are not just functional, but fully audit-ready and optimized for long-term growth.